Set up by hand
Security set up by whoever was there at the time, a little different at every business.
 Corporate & professional servicesLaw, accounting, finance and consulting firms, where client data and uptime are the business.
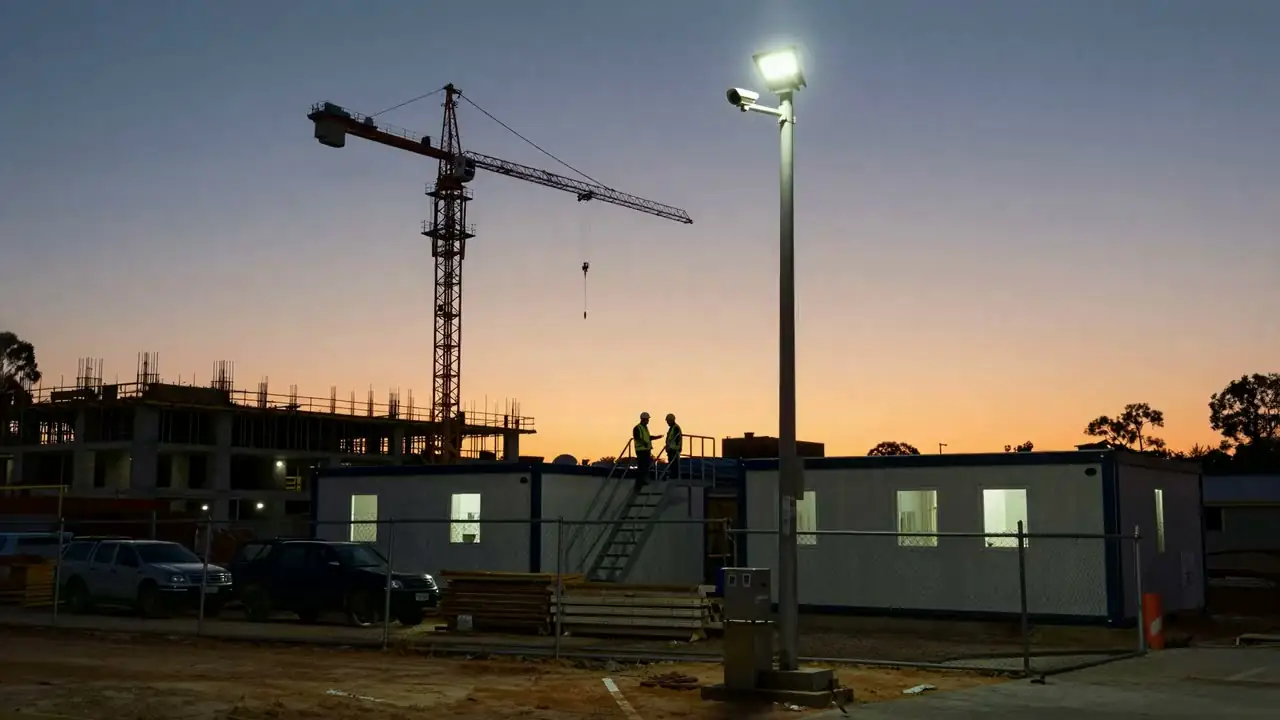 Construction & infrastructureSite offices that move every year, crews in the field, and compounds that need watching after hours.
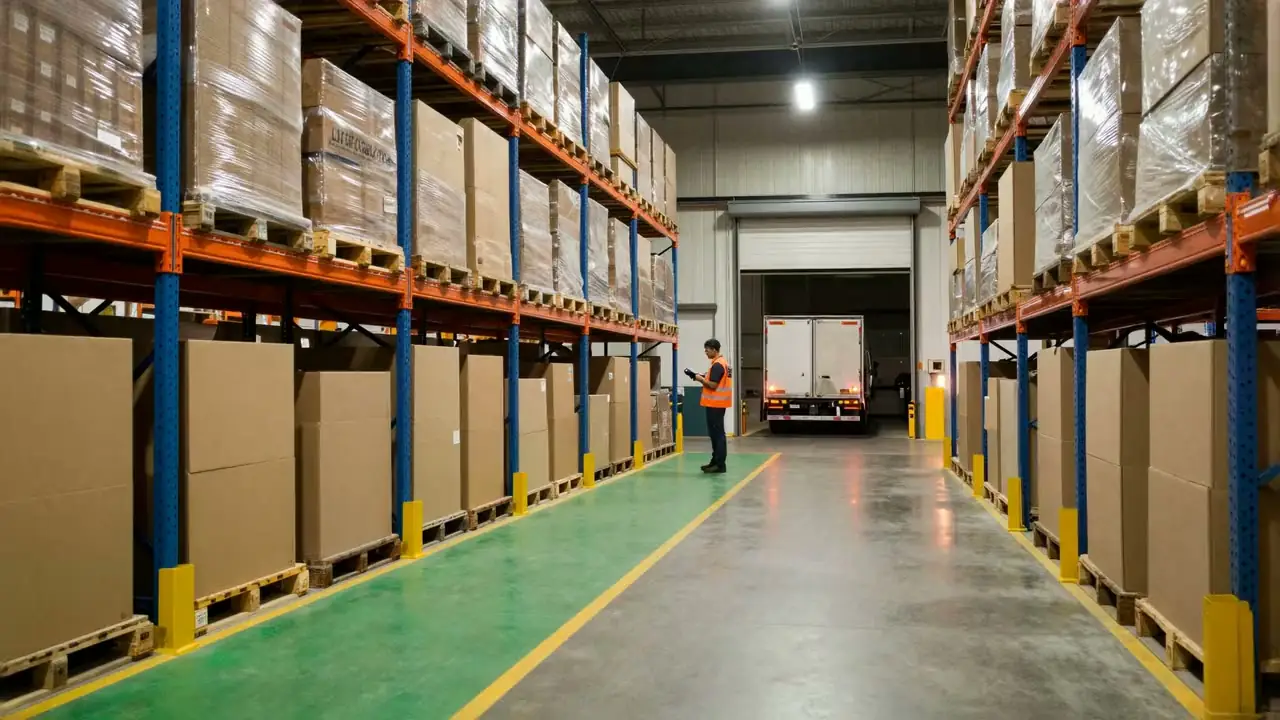 Logistics & warehousingDocks, yards and racking where people and vehicles share the same floor.
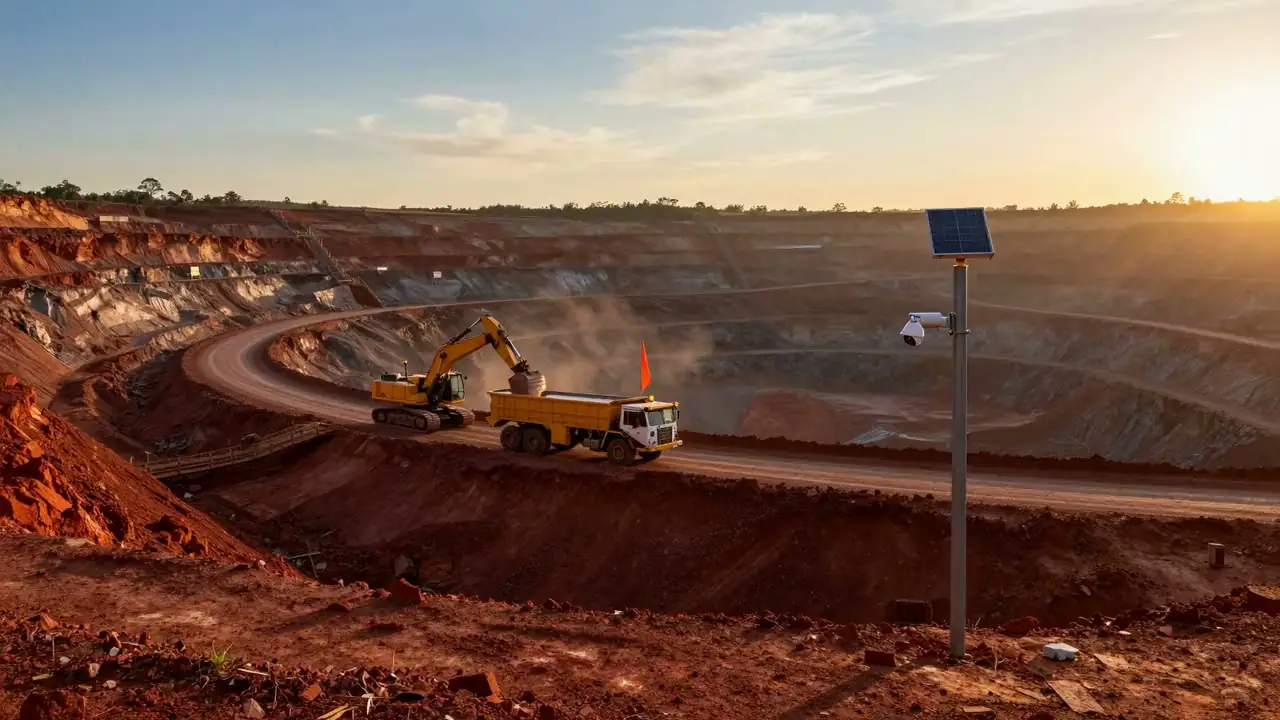 Mining & resourcesMines, quarries and resources sites, where remote crews, heavy vehicles and site systems all depend on the network.
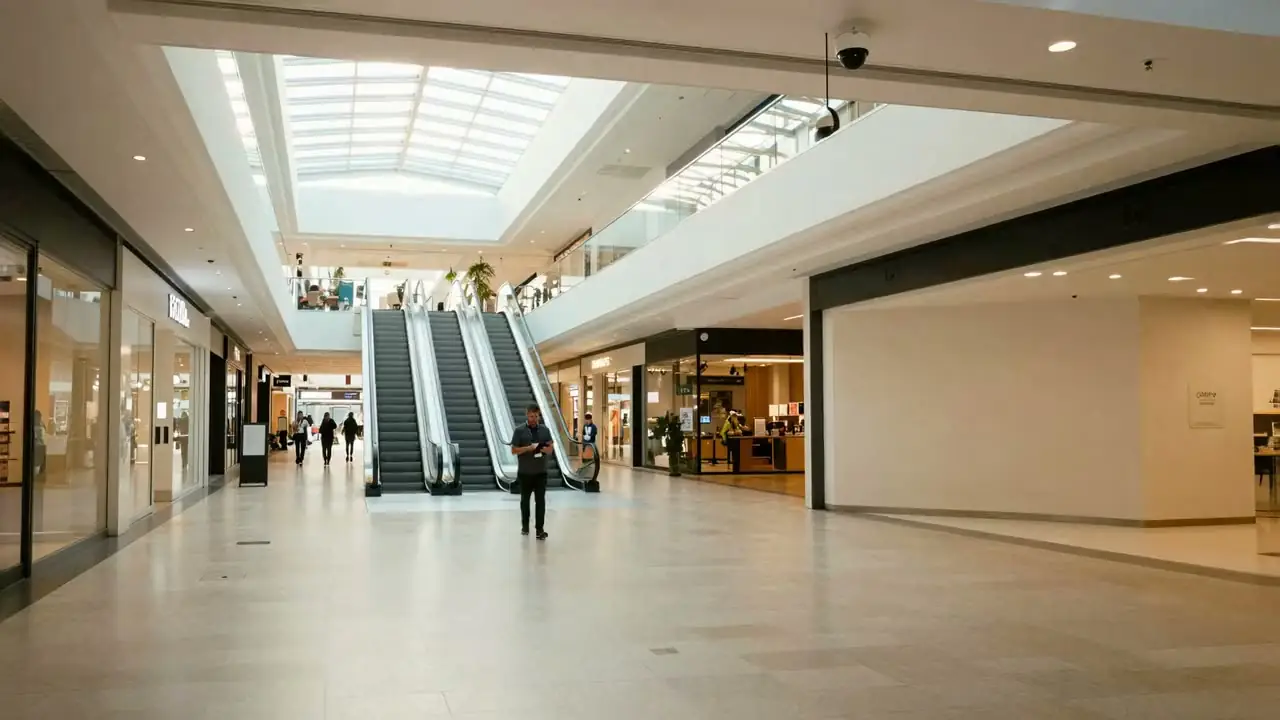 Retail & shopping centresMany sites, small teams on each, and cameras that should be doing more than recording.
 Aged careResidential aged care and retirement living.
 Healthcare & medicalClinics and practices with patient records to protect and systems that cannot go down.
The same security, switched on for every customer, from day one.
One tested set of Microsoft 365, computer and phone controls, checked every 12 hours and written up for your insurer.
Not because nobody tried. Because security set up by hand drifts, and nobody keeps the record.
Security set up by whoever was there at the time, a little different at every business.
A setting changed to fix one problem and never changed back. Nobody notices until it matters.
When an insurer asks what's switched on, the answer is a questionnaire and a best guess.
Here's how we take you from there to a baseline you can prove.
Five steps from your approval to your document, so the protection goes on without stopping anyone's work.
Your administrator approves a secure partner connection. We never ask for your admin password.
We list anyone who'd be blocked, such as an old phone, a shared login or a personal laptop, and sort each one out with you first.
Multi-factor sign-in and the email and account controls are switched on for everyone.
Each computer is set up and checked; device rules start once every one is ready.
Your Cyber Security Baseline, with every control, its evidence, and any gaps you carry.
Multi-factor sign-in for everyone on every app. Passkeys for administrators. Old methods that skip MFA are switched off.
Phishing and malware filtering, links checked when they're clicked, outside email labelled, and no automatic forwarding outside the business.
Records that stop others sending email as you, brought in stages so your real email keeps flowing.
Updates applied and monitored, disk encryption, the firewall on, no local admin rights for staff.
Work data stays inside the Microsoft 365 apps behind a PIN. We never take over a personal phone.
The same settings for every customer on the same plan, checked twice a day, and changed only through a tested release.
Every customer on the same plan gets the same tested settings. Nothing is set up differently by hand for one business.
If a control is changed, it's put back automatically and we're alerted.
Every change is checked automatically and approved before release, and reaches every customer on the plan at once, never one business by hand.
The Essential Eight ↗ is the Australian Signals Directorate's baseline for protecting a business. This is where each plan stands today.
| Strategy | Essential | Advanced | Premium |
|---|---|---|---|
| Multi-factor authentication | In place | In place | In place |
| Patch applications | |||
| Patch operating systems | |||
| Restrict administrative privileges | |||
| Regular backups | Not yet | ||
| Application control | Not yet | Not yet | Not yet |
| Restrict Microsoft Office macros | Not yet | Not yet | Not yet |
| User application hardening | Not yet | Not yet | Not yet |
Covered: switched on and looked after on every plan, with some of ASD’s detail still being finished. ✓ In place: meets every part of ASD’s strategy. This is not a maturity level: only an assessor testing each control can establish one. Advanced and Premium have the same security controls; Advanced adds daily backup of every mailbox and OneDrive.
Switch them on to see every plan reach all eight covered. Talk to us and we'll scope it for your business.
Approved programs only, Office macros blocked and apps locked down, part of the way, on every work computer.
Adds backup of your computers to the email and file backup, every day, to a copy ransomware can't touch.
Microsoft Purview finds files like customer details, payroll and contracts, labels them, and stops them leaving the business by mistake. Beyond the Essential Eight.
When an insurer, auditor or assessor asks how you're protected, you hand them your Cyber Security Baseline. It sets out what's in place, maps it to the frameworks they ask about, and names any gaps, so the conversation starts with facts, not a questionnaire.
It supports an assessment; it isn't one. Only an assessor testing each control can confirm a maturity level or a certification.
ASD published the ASD Essentials on 15 October 2026 as the next step on from the Essential Eight. Both stay in use during the transition. Your baseline document maps our controls to both, so nothing needs redoing when ASD makes the switch.
Read ASD's announcement ↗A preview of the Cyber Security Baseline for the Advanced plan: the summary, where it stands on the Essential Eight, a first look at the controls and the ISO 27001 and ASD Essentials mappings, and the risks section. Client details are placeholders.
Customers get the full document, including the technical register, for their own business. An auditor or insurer can ask us for the evidence behind any line.
See more. Respond faster. Stay secure.